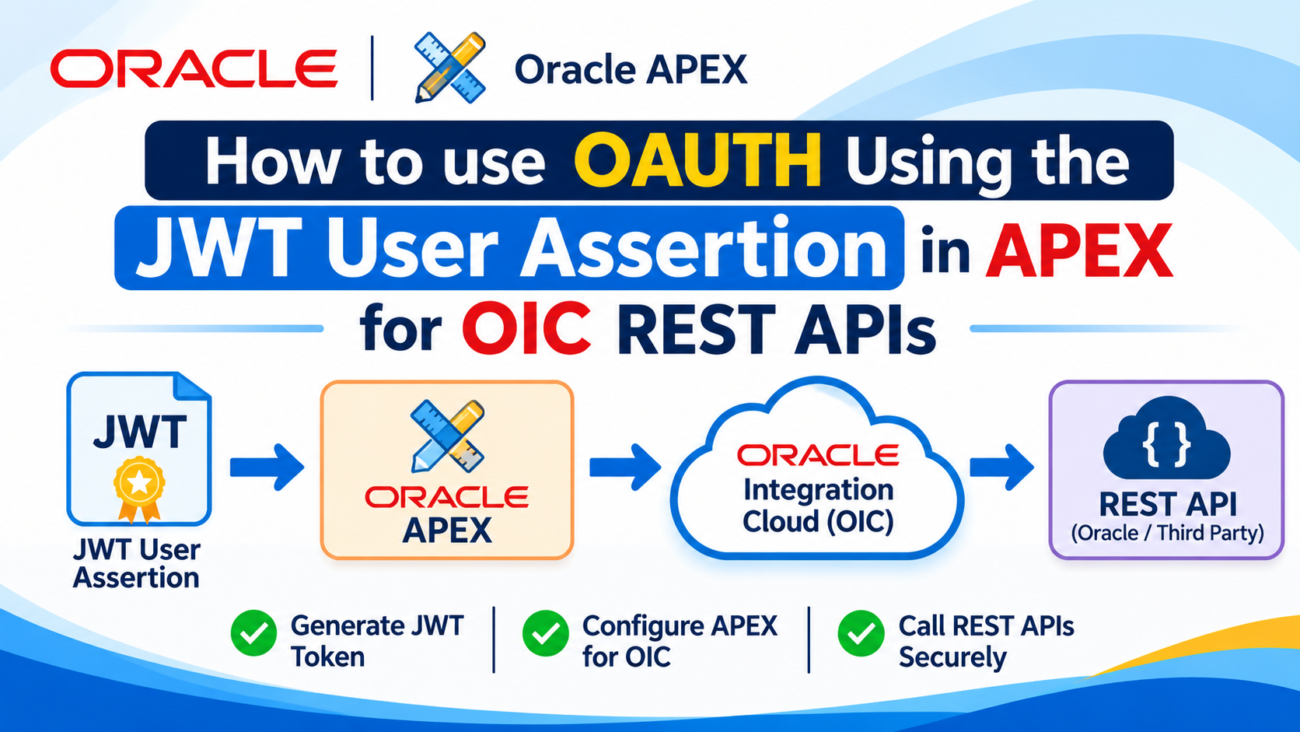
This article will demonstrate how to use OAUTH using JWT User Assertion in APEX for OIC REST APIs.
What is JWT User Assertion?
- JWT User Assertion is a security token that represents a user’s identity and is issued by a trusted identity provider.
- It is digitally signed and includes claims such as User ID (sub), issuer (iss), audience(aud) and expiration(exp)
- Used in Oauth2.0 flows. It allows security identity propagation and token exchange without direct user interaction.
Step1: Generate the key
- Generate the self-Signed key pair
Open command prompt and run below command to generate self-signed key pair
- keytool -genkey -keyalg RSA -alias demojwtkey -keystore sampleKeystore.jks -storepass Oracle@123 -validity 365 -keysize 2048
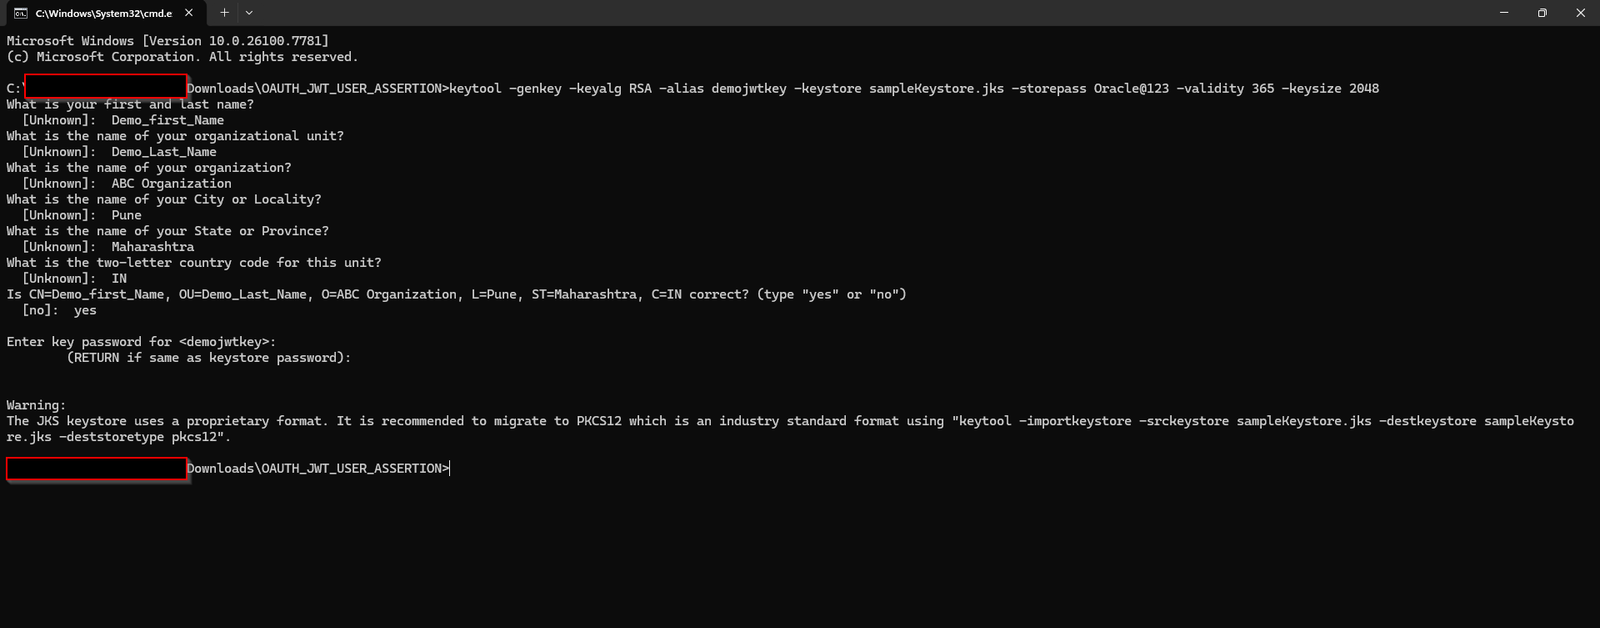
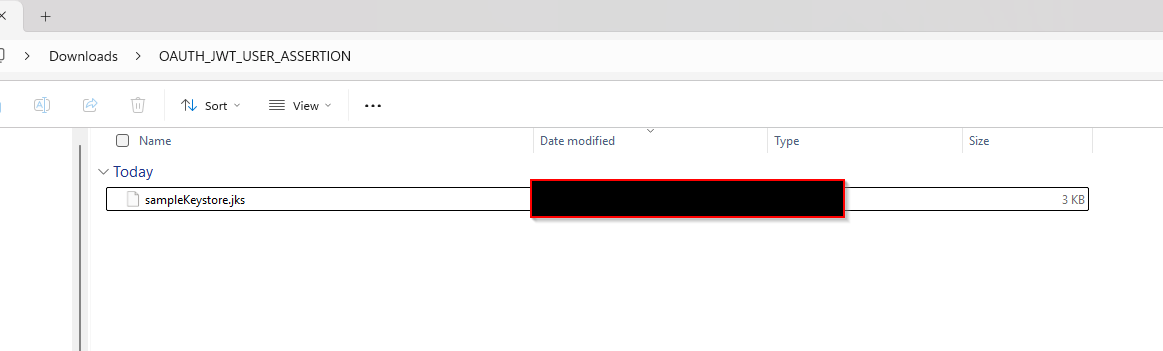
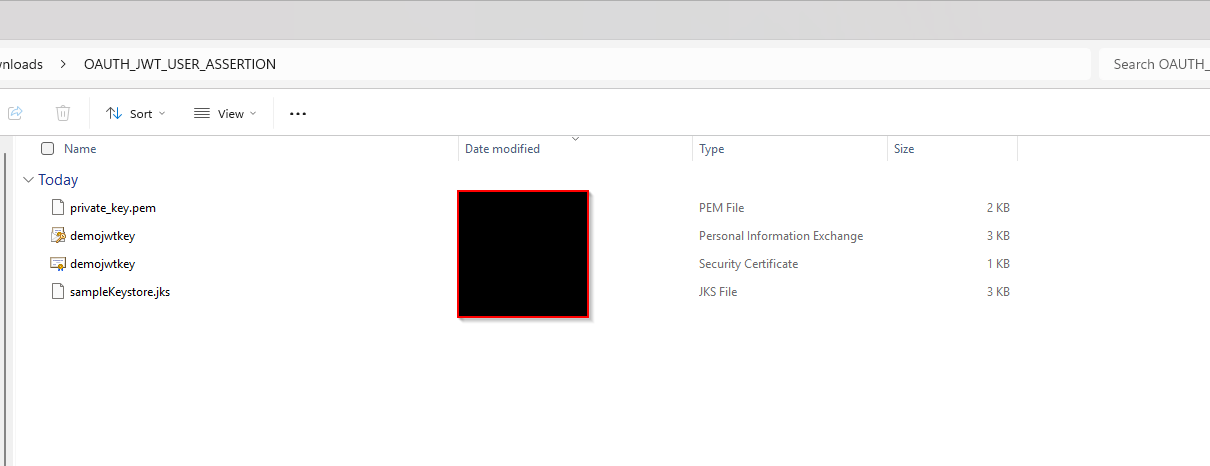
This will generate sampleKeystore.jks file as shown below:
2. Export the public key for signing the JWT assertion
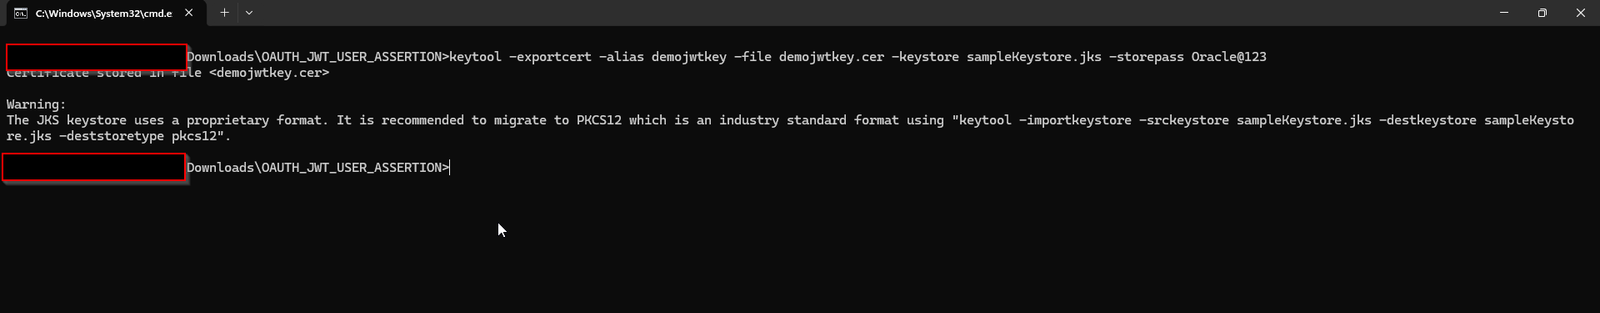
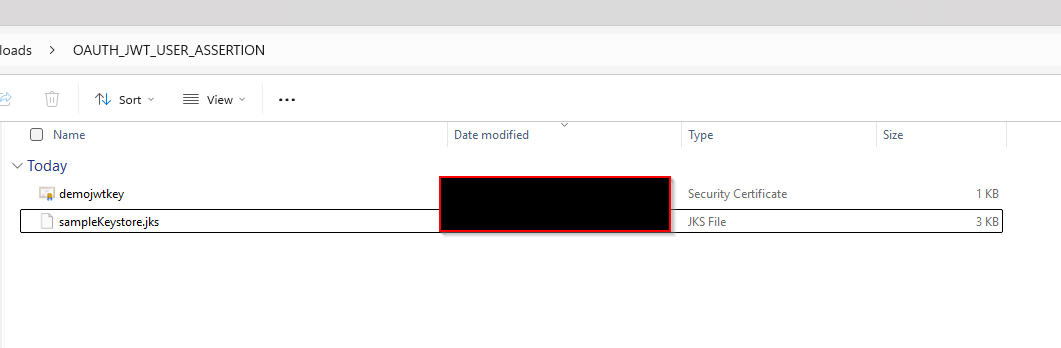
- keytool -exportcert -alias demojwtkey -file demojwtkey.cer -keystore sampleKeystore.jks -storepass Oracle@123
3. Convert the keystore to P12 format:
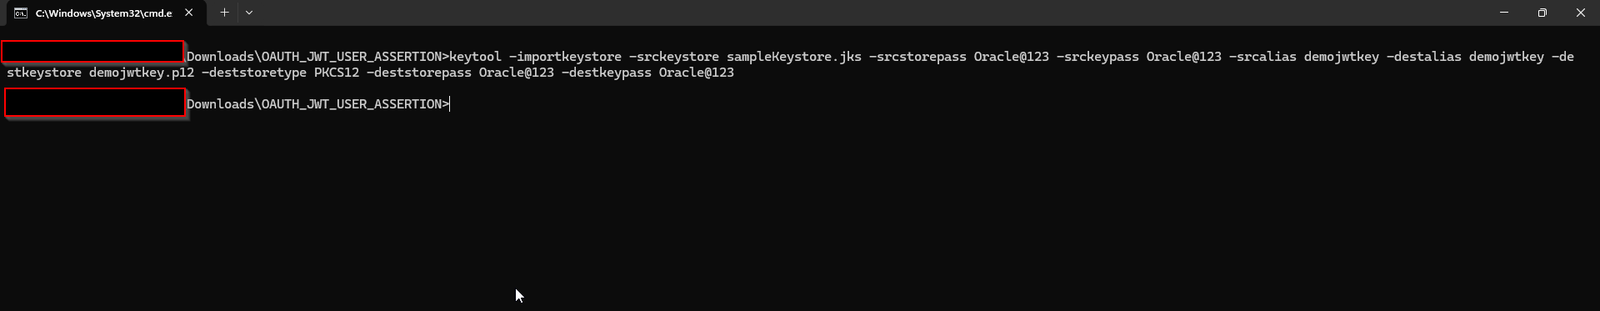
- keytool -importkeystore -srckeystore sampleKeystore.jks -srcstorepass Oracle@123 -srckeypass Oracle@123 -srcalias demojwtkey -destalias demojwtkey -destkeystore demojwtkey.p12 -deststoretype PKCS12 -deststorepass Oracle@123 -destkeypass Oracle@123

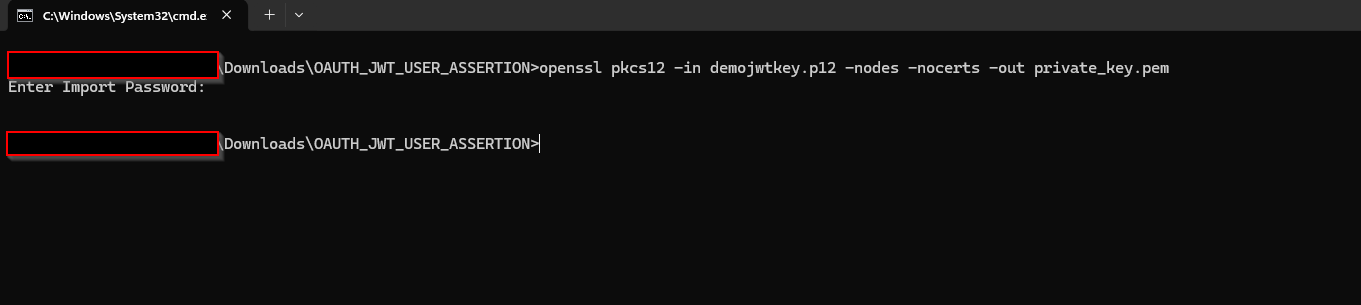
4. Export the private key from P12 key store:
- openssl pkcs12 -in demojwtkey.p12 -nodes -nocerts -out private_key.pem
******Install openssl before running this command.
5. Convert cert file to P12 Format:
- openssl x509 -inform DER -in demojwtkey.cer -out demojwtkey_cert.pem
Step2: Crate Confidential Application in IDCS.
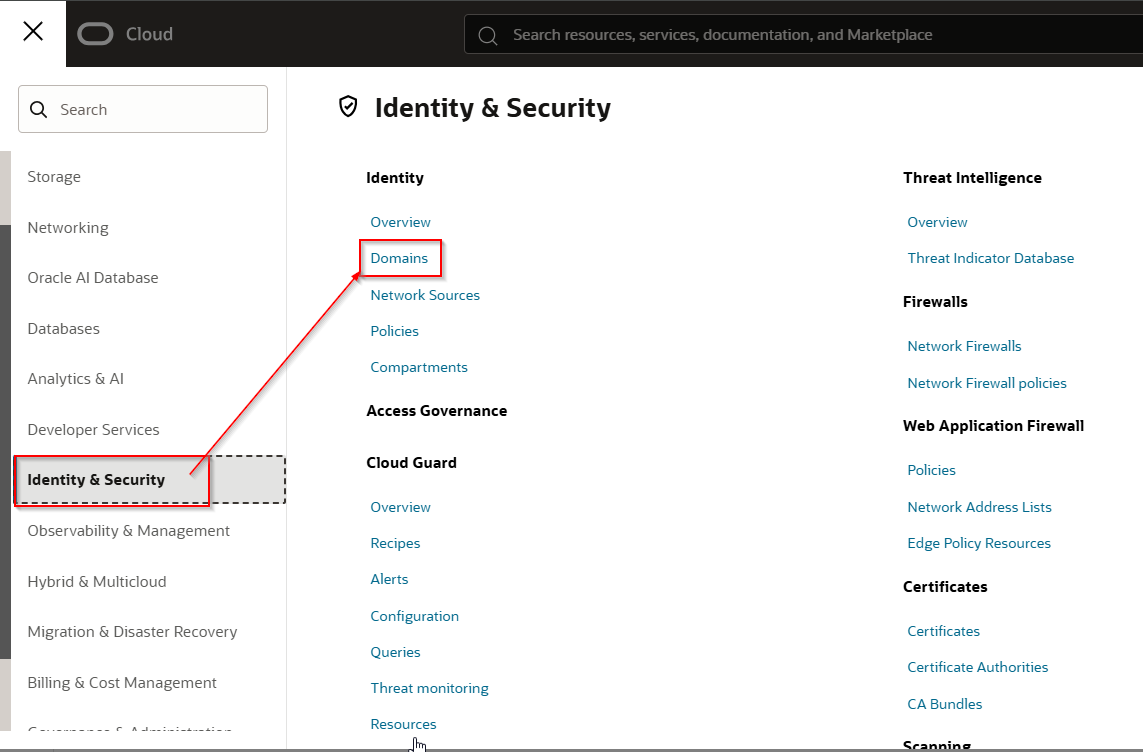
Login to OCI console.
Navigate to Identity & Security —>Domains
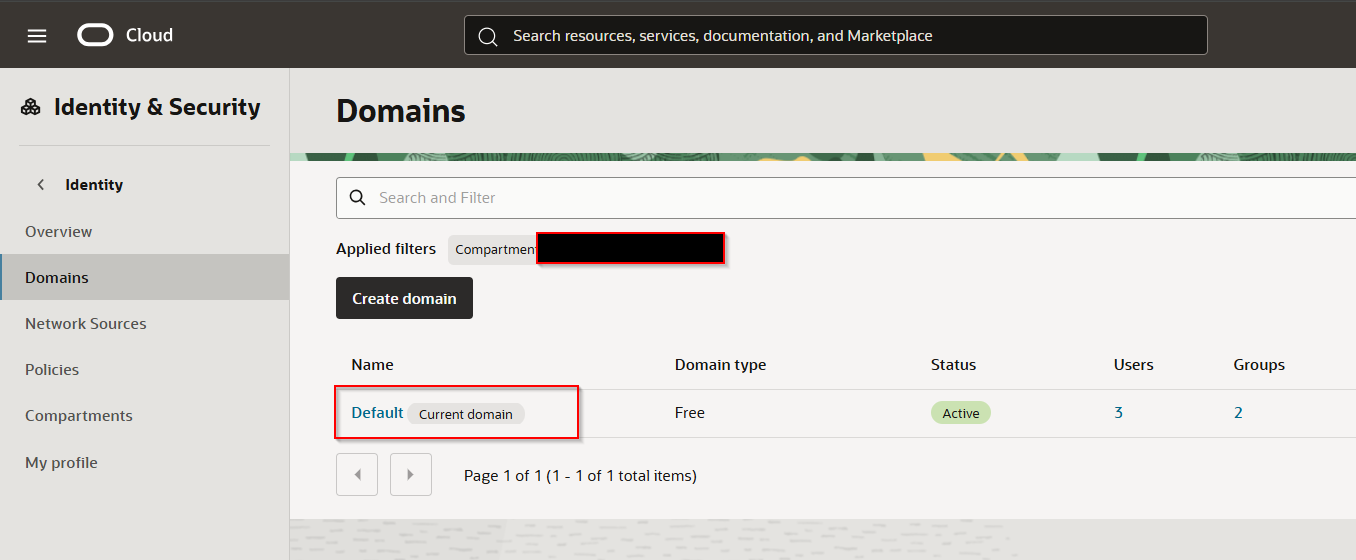
Select the domain.
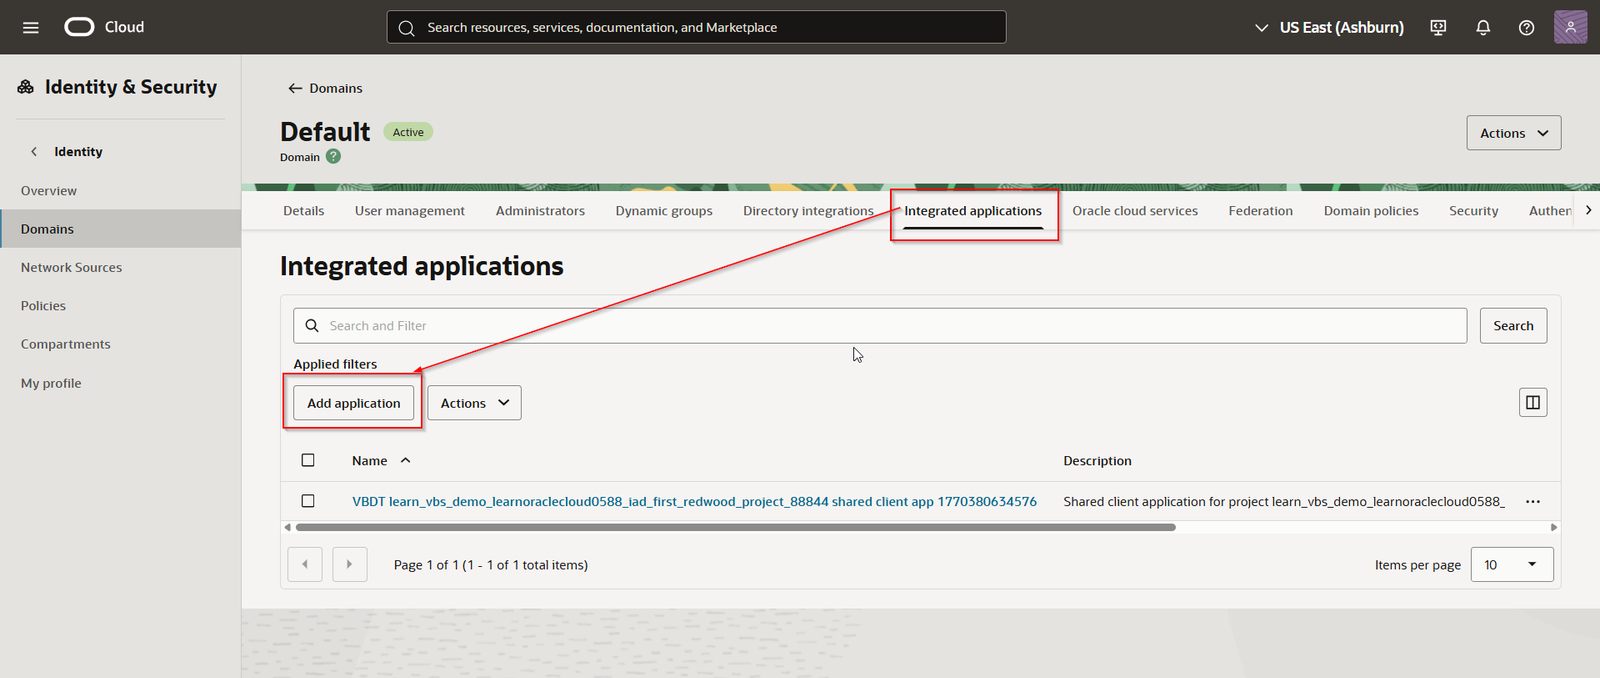
Navigate to Integrated applications —> Add Application.
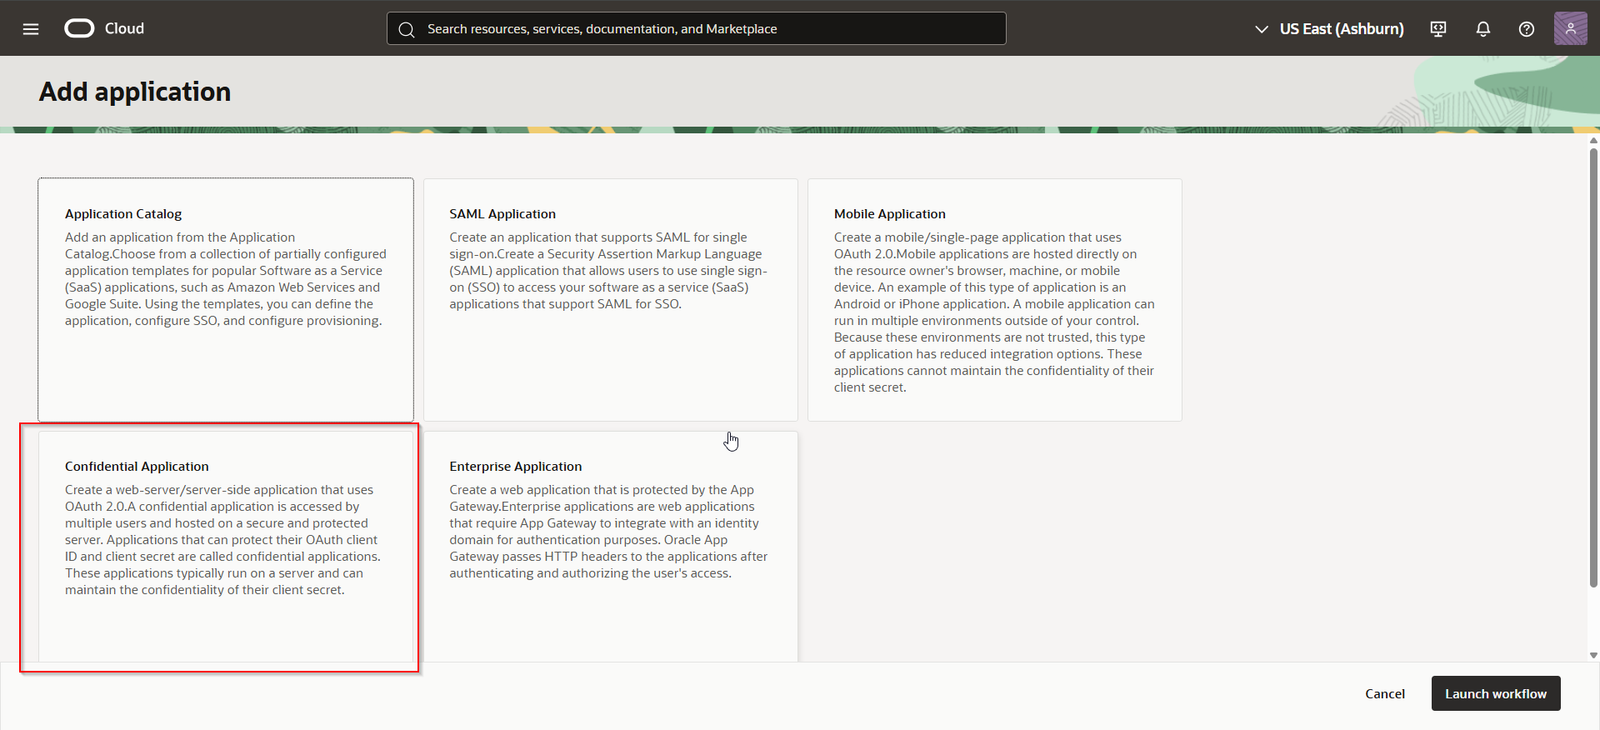
Select “Confidential Application” and click Launch workflow.
Provide the name and description to application and click Submit.

Navigate to OAuth configuration —>Edit OAuth configuration


select “Configure the application as a client now” and authorization as “JWT Assertion”

Select checkbox for Trusted and on behalf of

Click on Import Certificate to upload signing certificate which is generated in earlier step.

Click on Import.
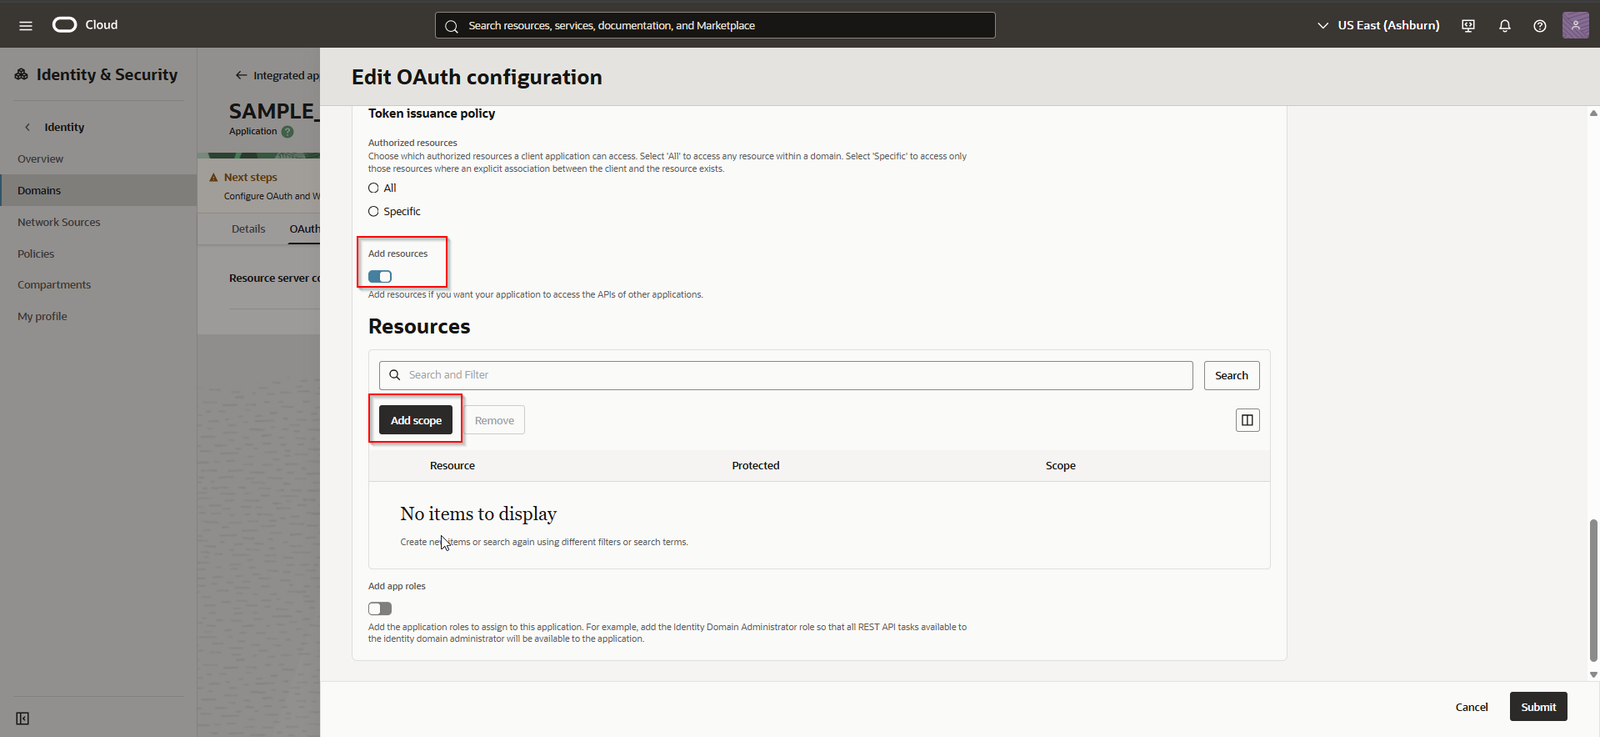
Enable “Add resources” and Click on Add Scope.

Select all scopes for OPA and click on Add.
Select scope for OIC if we want to enable JWT for OIC REST API.

Click on Submit.
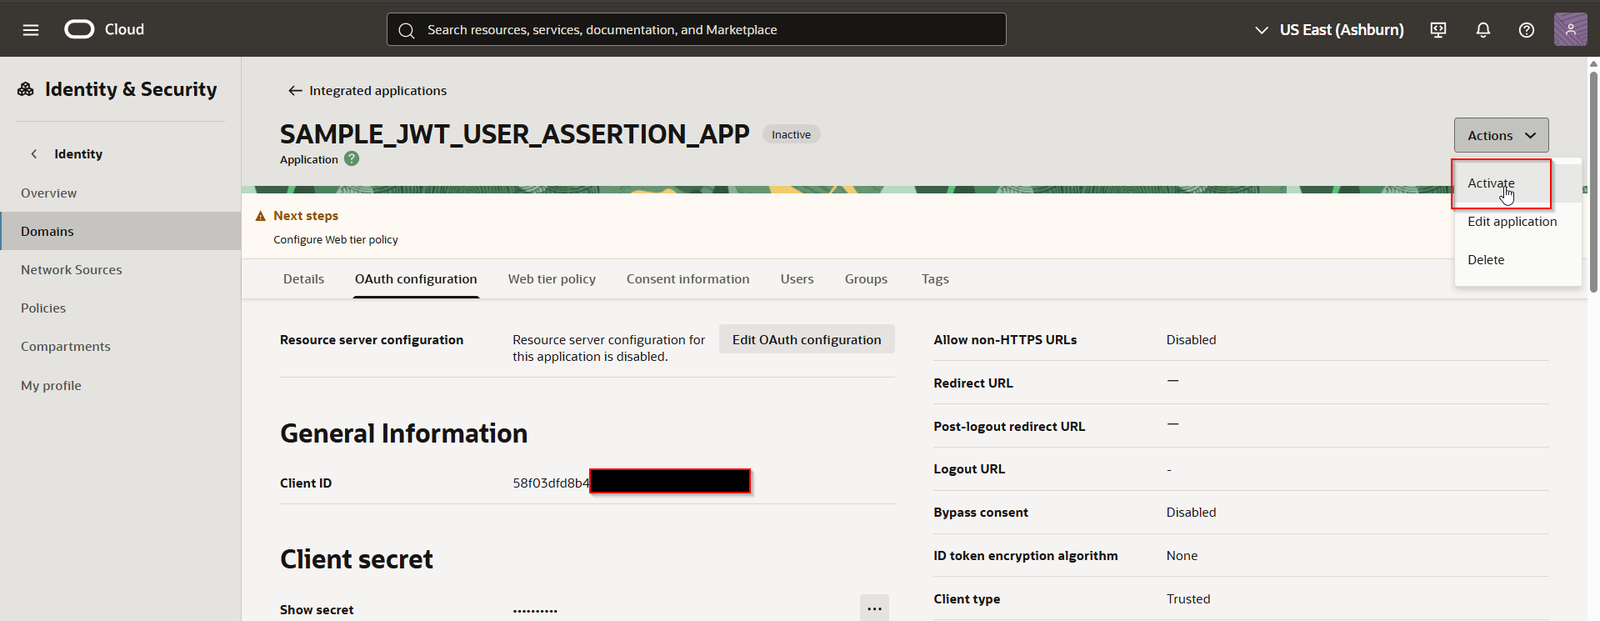
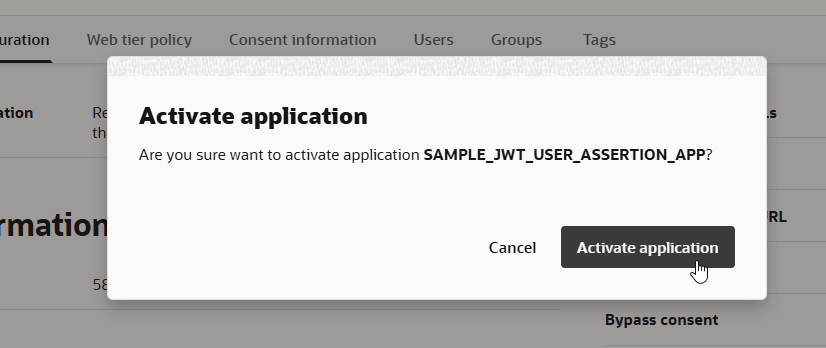
Activate the application.

Step3: Upload Certificate as Trusted Partner Certificate.
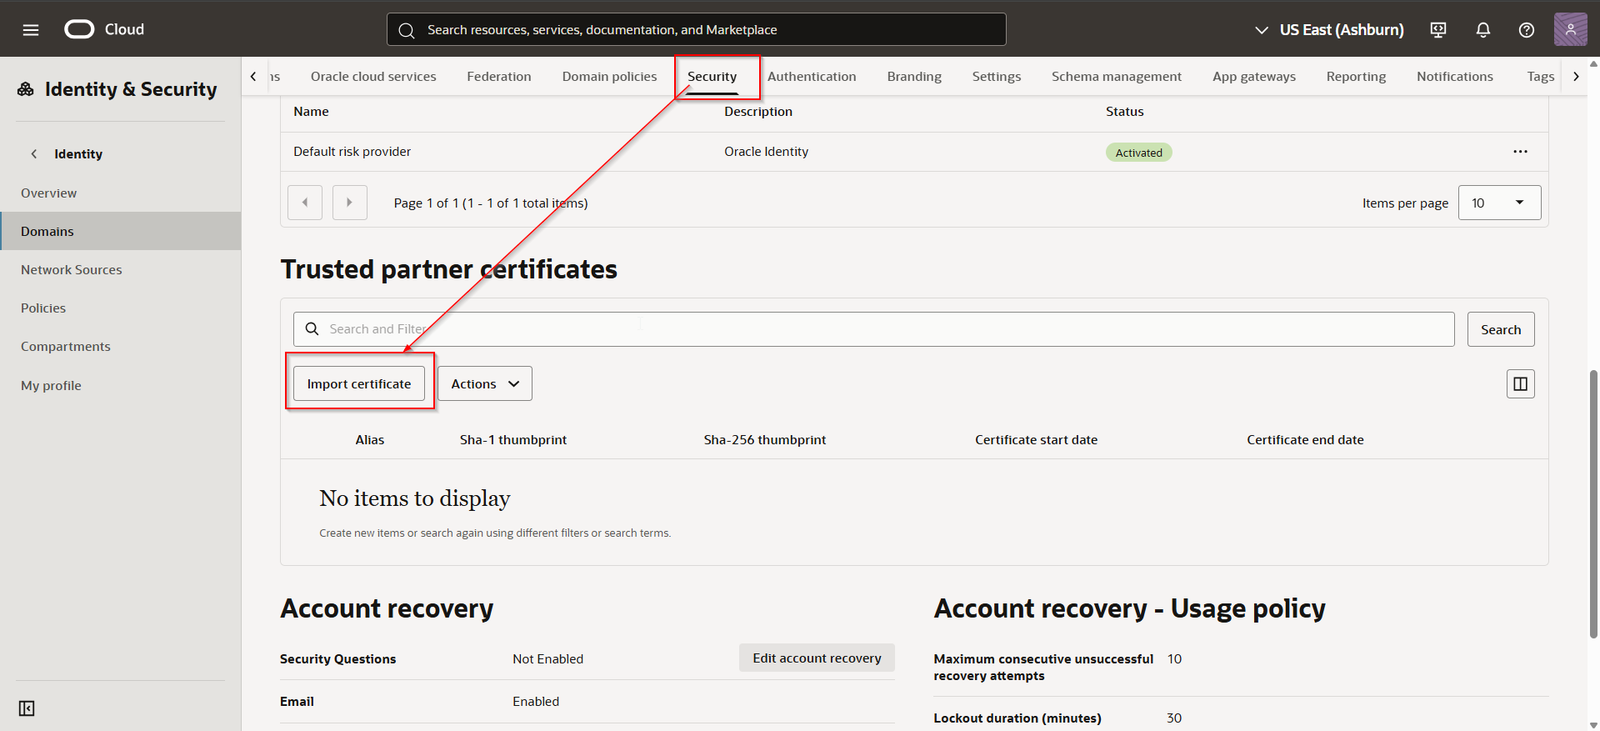
Navigate to domain —>Security —>Trusted partner certificates —>Import certificate.
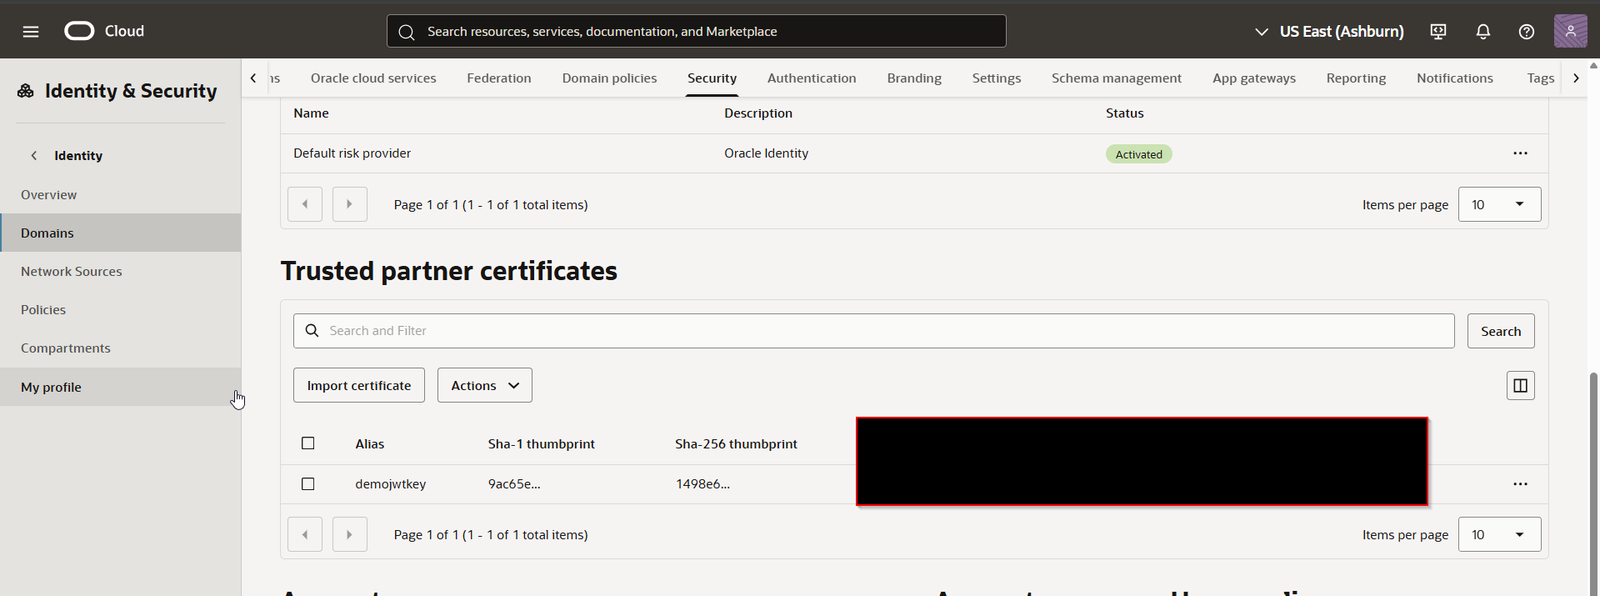
Import same certificate which is uploaded in earlier step.
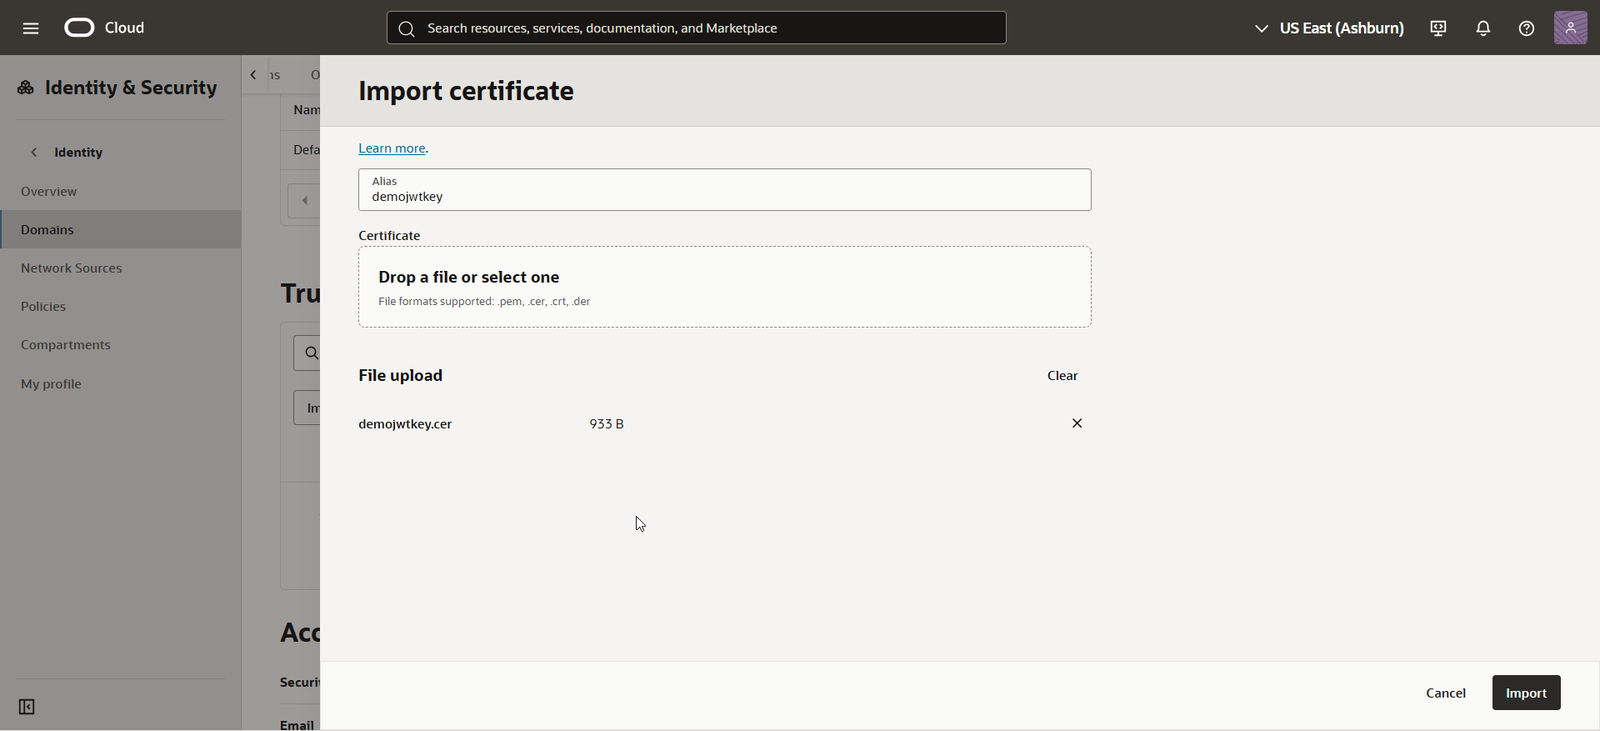
Click Import.
Step4: Create Simple Application in APEX.
Login to Oracle APEX workspace —>App Builder –>Create.
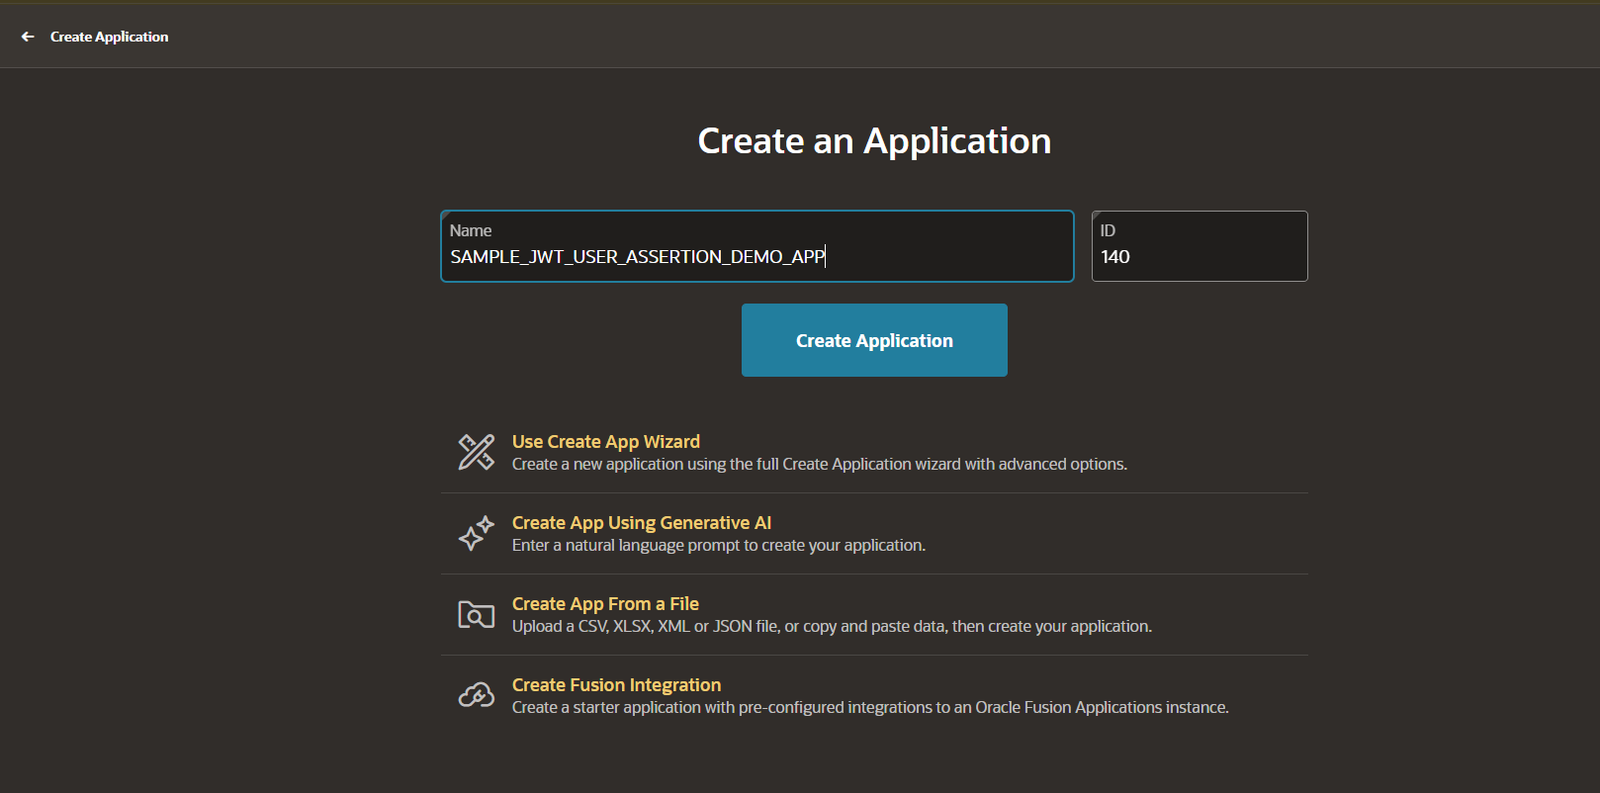
Click on Create Application.
Step5: Create Web Credentials for JWT User Assertion.
For enabling OUATH2.0 JWT user assertion in oracle APEX, we need to create two web credentials as follows.
Navigate to Shared Components —-> Credentials


Click on Create-to-create new Web Credentials.
(A) User Assertion Signing Certificate:
Create web credentials of Authentication type as “User Assertion Signing Certificate” with below details:

Provide details as per the table below:
| Configuration | Value / Instructions | Description |
|---|---|---|
| Name |
USER_ASSER_SIGN_CERTI_DEMO
|
Provide any valid name. |
| Static ID |
user-asser-sign-certi-demo
|
Automatically generated. |
| Authentication Type | User Assertion Signing Certificate | Specifies the authentication mechanism. |
| Certificate |
Provide the contents of the
demojwtkey_cert.pem
file, which we converted from the
demojwtkey.cert file.
|
Provide the public certificate content. |
| Private Key |
Provide the contents of the
private_key.pem file.
|
Provide the corresponding private key. |
| Audience List | https://identity.oraclecloud.com/ | Hardcoded audience value. |
| Certificate Alias | Provide any valid alias name. | Used to identify the certificate. |
(B) Signed User Assertion:
Create web credentials of Authentication type as “Signed User Assertion” with below details:
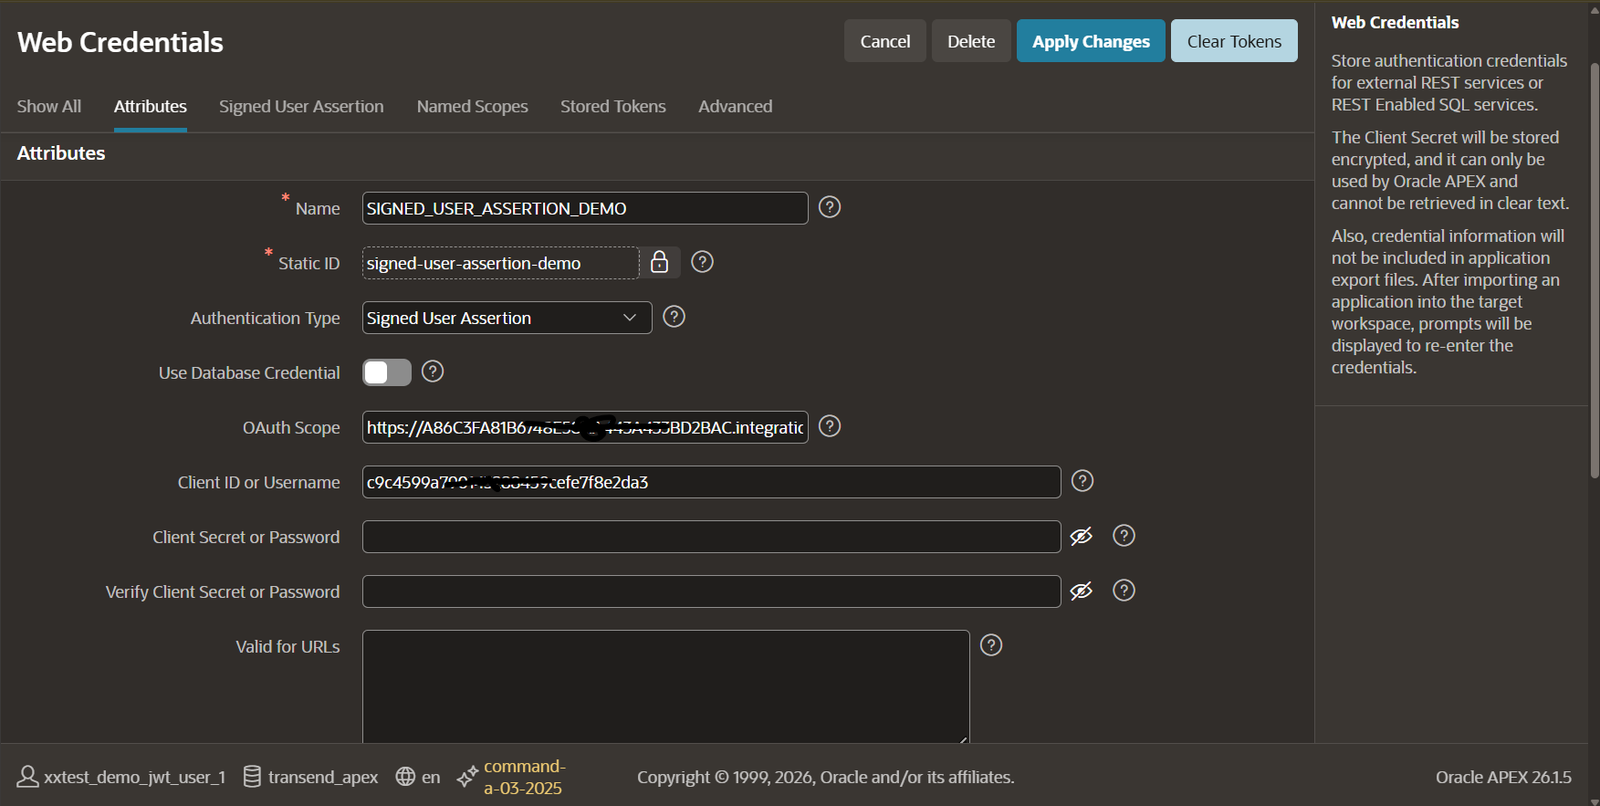
Provide details as per the table below:
| Configuration | Value / Instructions | Description |
|---|---|---|
| Name |
SIGNED_USER_ASSERTION_DEMO
|
Provide any valid name. |
| Static ID |
signed-user-assertion-demo
|
Automatically generated. |
| Authentication Type | Signed User Assertion | Specifies the authentication mechanism. |
| Use Database Credentials |
No
|
Do not enable this option. |
| OAuth Scope |
https://XXXXXXXX.integration.us-chicago-1.ocp.oraclecloud.com:443/process
|
Provide the scope for OPA copied from the confidential application. |
| Client ID | Obtain the Client ID from your confidential application. | Get Client ID from the confidential application. |
| Client Secret | Provide the Client Secret from your confidential application. | Get Client Secret from the confidential application. |
| Verify Client Secret or Password | Provide the Client Secret from your confidential application. | Get Client Secret from the confidential application. |
Now go to Signed User Assertion tab and select Web credential which we have created in earlier step.
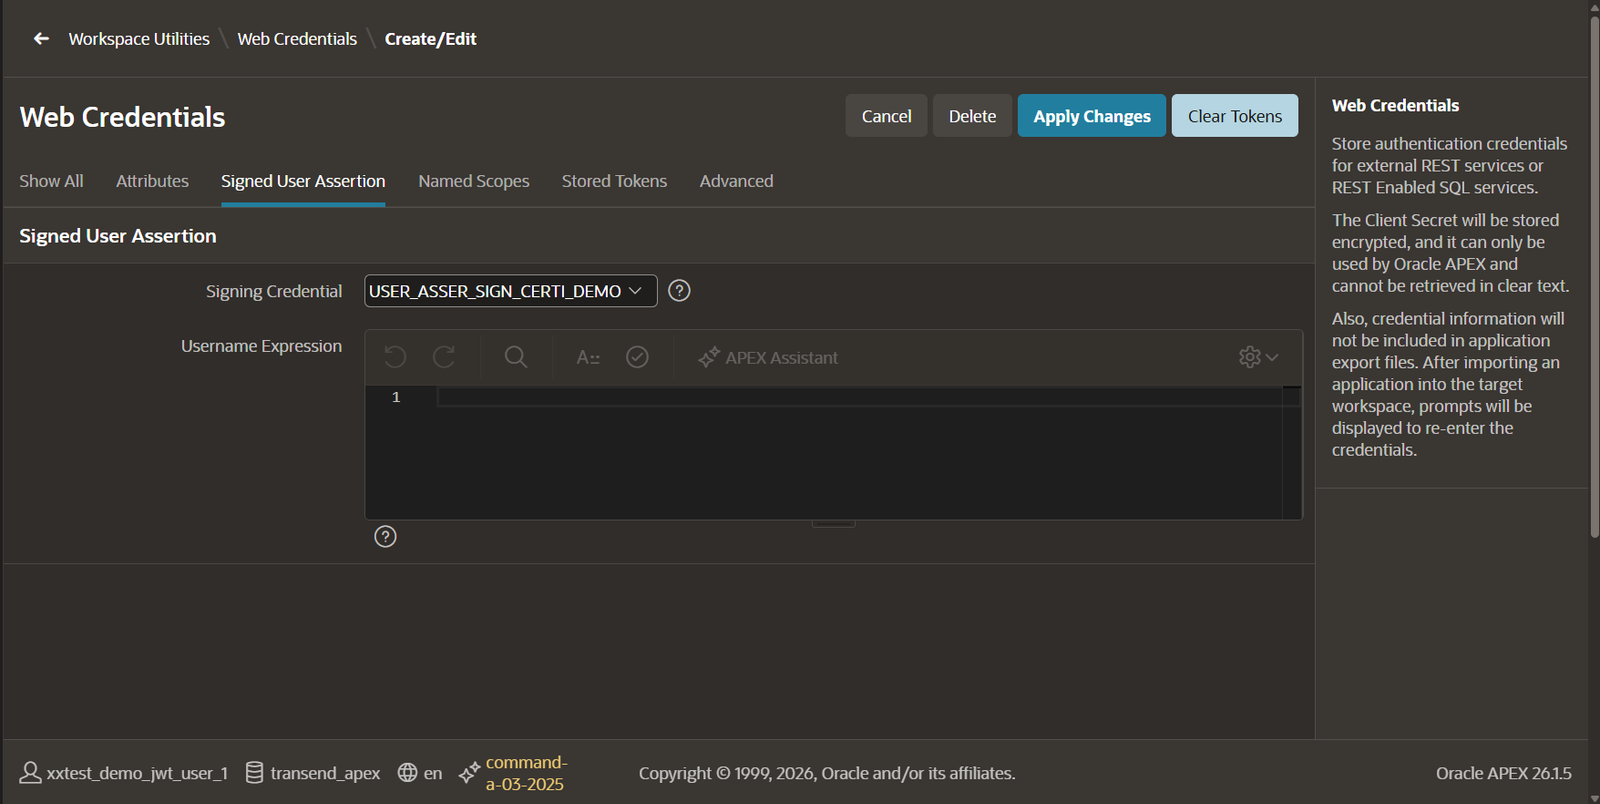
Click on Apply changes.
Step6: Create Simple OPA process Application.
Create two users in IDCS for OPA access as shown below:
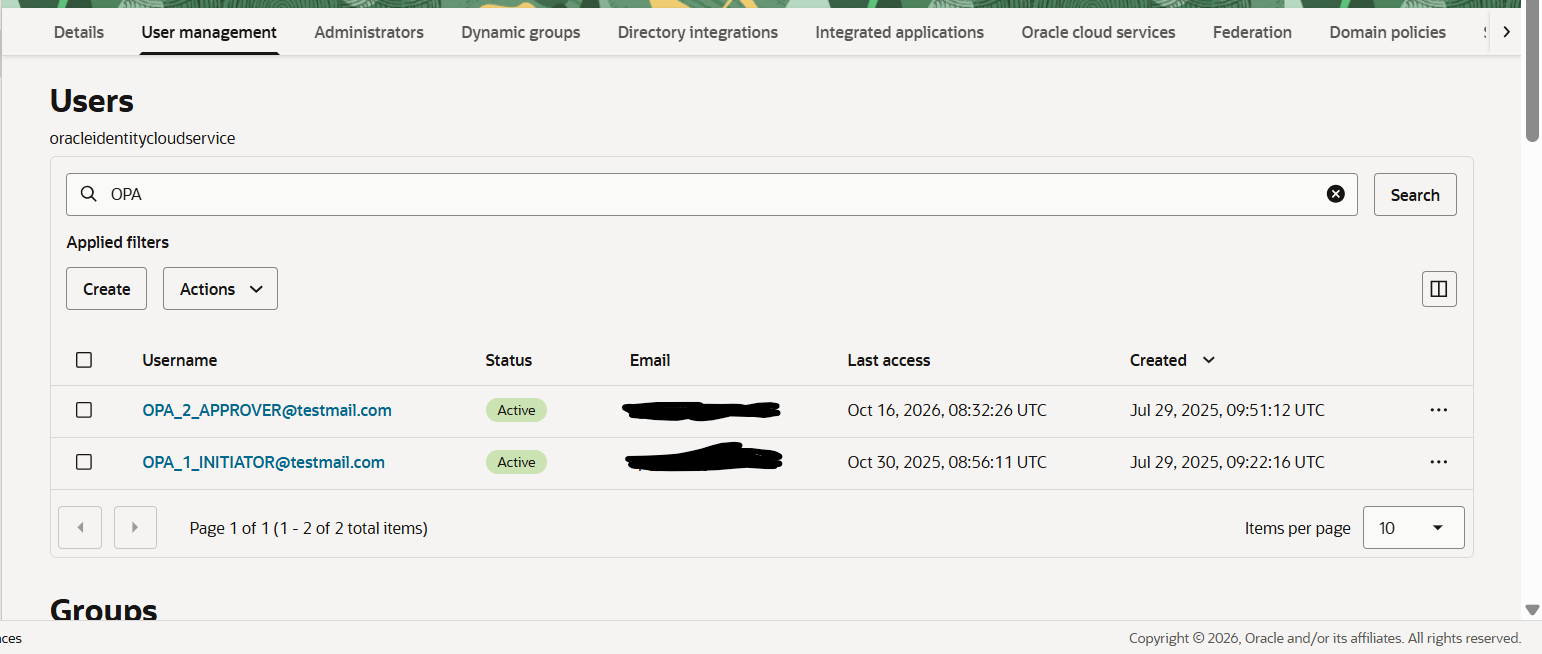
Navigate to Oracle Process Automation.
Create very simple application as shown below:

Here we have the process flow:
Initiator (OPA_1_INITIATOR@testmail.com) will initiate leave requests with the details below:
- Leave type
- Number of Days.
Once Initiator submits requests, it will go to approver (OPA_2_APPROVER@testmail.com).
Once approve or Reject request, process flow will be completed.
We will call this OPA process from Oracle APEX application with JWT user assertion.
Step7: Create Users in Oracle APEX.
Create users with same username below in oracle APEX.
Navigate to Manage Users and Groups
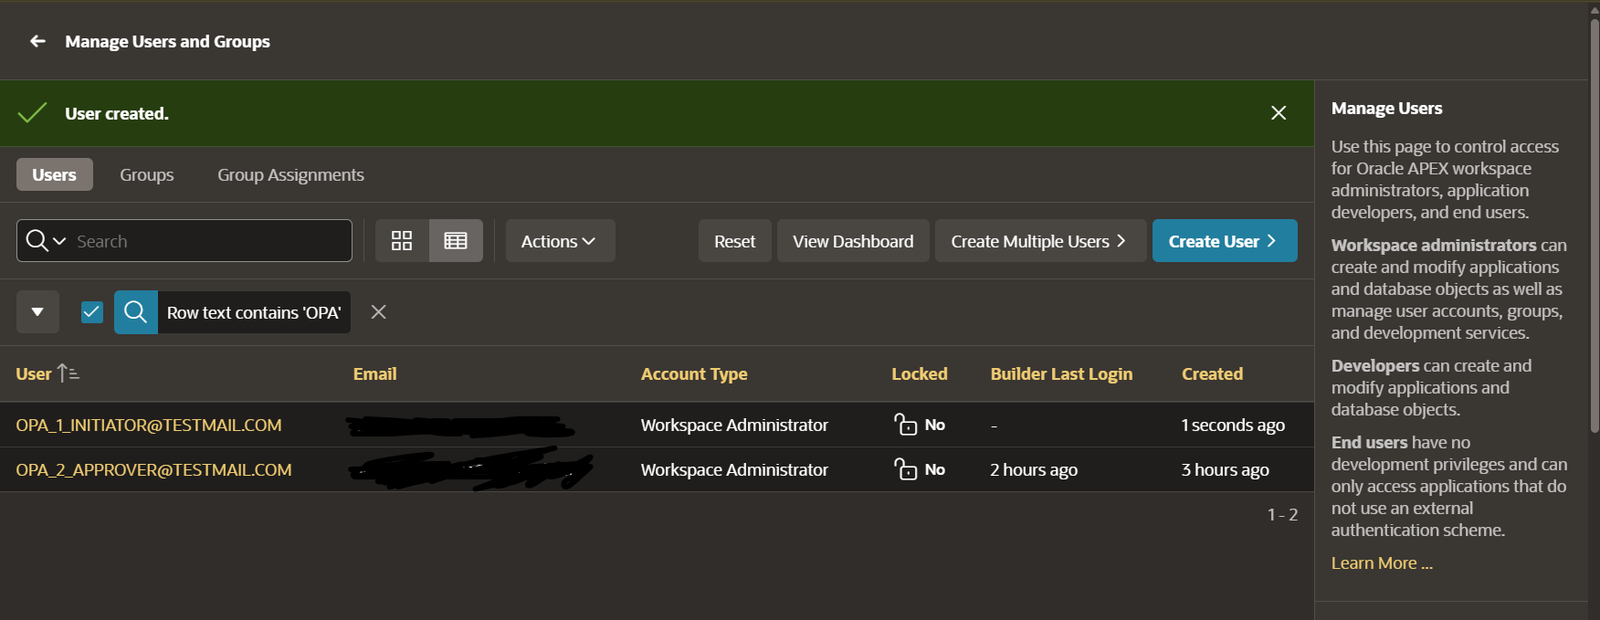
Step8: Create Simple Leave Request Application in Oracle APEX.
Let us create very simple leave request application in oracle APEX. The application will contain leave request page and request approval page as shown below:
- Leave Request Approval Page:
In this page user will create leave request.

Add below PLSQL code to call OPA REST API when click on Submit button.
This will use Web credentials which we have created in earlier steps.
PLSQL Code for Submit Button:
- DECLARE
- l_response CLOB;
- l_body CLOB;
- BEGIN
- l_body := '{
- "params": {
- "applicationName": "DEMO_APPROVAL_APP",
- "processName": "LeaveRequestApproval"
- },
- "dataObject": {
- "submitRequestFormArgs": {
- "leaveType": "'||:P2_LEAVE_TYPE||'",
- "numberofDays": "'||:P2_NUMBER_OF_DAYS||'"
- }
- }
- }';
- apex_web_service.g_request_headers.DELETE;
- apex_web_service.G_request_headers(1).NAME := 'Content-Type';
- apex_web_service.G_request_headers(1).VALUE := 'application/json';
- apex_web_service.G_request_headers(2).NAME := 'Accept';
- apex_web_service.G_request_headers(2).VALUE := 'application/json';
- l_response := apex_web_service.Make_rest_request( p_url => 'https://opa-oic-XXXX-XXXXXXXXXX-ord.process.oci.oraclecloud.com/process/api/v1/instances', p_http_method => 'POST', p_credential_static_id => 'signed-user-assertion-demo', p_token_url => 'https://idcs-XXXXXXXXX.identity.oraclecloud.com:443/oauth2/v1/token', p_body => l_body );
- dbms_output.Put_line( dbms_lob.Substr(l_response, 32000, 1) );
- :P1_RESPONSE :=l_response;
- END;
Once OPA leave request is submitted, it will generate Task ID.
- Approve Request Page:
In this page, approver will approve leave request based on task id.

Note:
This is demo application hence we will get Task ID from OPA once request is submitted manually. But in real time, we can get details using REST API.
Add below PLSQL code to call OPA REST API to approve request when click on Approve Request button.
- DECLARE
- l_response CLOB;
- l_body CLOB;
- BEGIN
- l_body := '{
- "outcome": "APPROVE",
- "comment": "Approved"
- }';
- apex_web_service.g_request_headers.DELETE;
- apex_web_service.G_request_headers(1).NAME := 'Content-Type';
- apex_web_service.G_request_headers(1).VALUE := 'application/json';
- apex_web_service.G_request_headers(2).NAME := 'Accept';
- apex_web_service.G_request_headers(2).VALUE := 'application/json';
- l_response := apex_web_service.Make_rest_request( p_url => 'https://opa-oic-XXXX-XXXXXXXX-ord.process.oci.oraclecloud.com/process/api/v1/tasks/'||:P3_TASK_ID||'/complete', p_http_method => 'POST', p_credential_static_id => 'signed-user-assertion-demo', p_token_url => 'https://idcs-XXXXX.identity.oraclecloud.com:443/oauth2/v1/token', p_body => l_body );
- dbms_output.Put_line( dbms_lob.Substr(l_response, 32000, 1) );
- :P1_RESPONSE :=l_response;
- END;
Step9: Test the application.
Login to oracle APEX application with OPA_1_INITIATOR@testmail.com and create leave request.
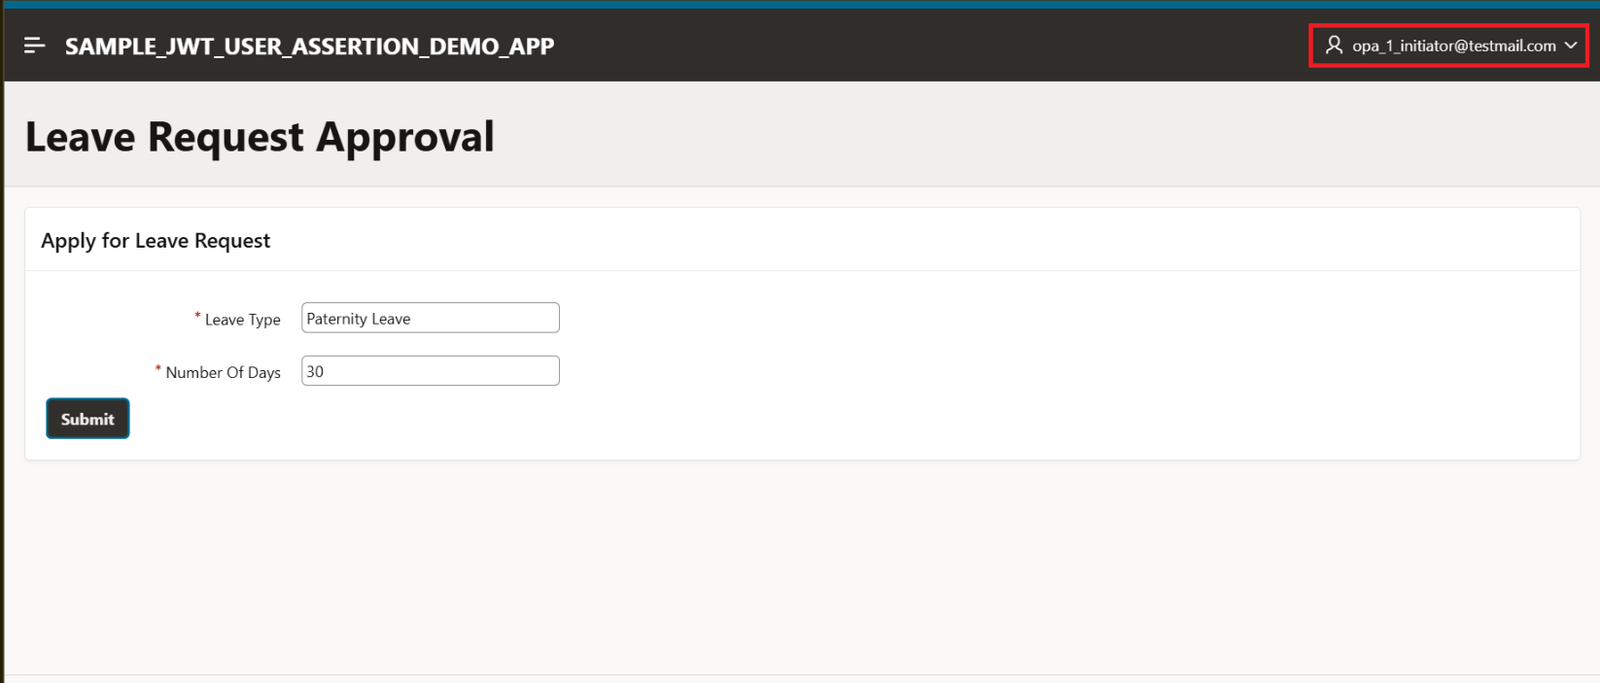
Provide details and click on Submit.
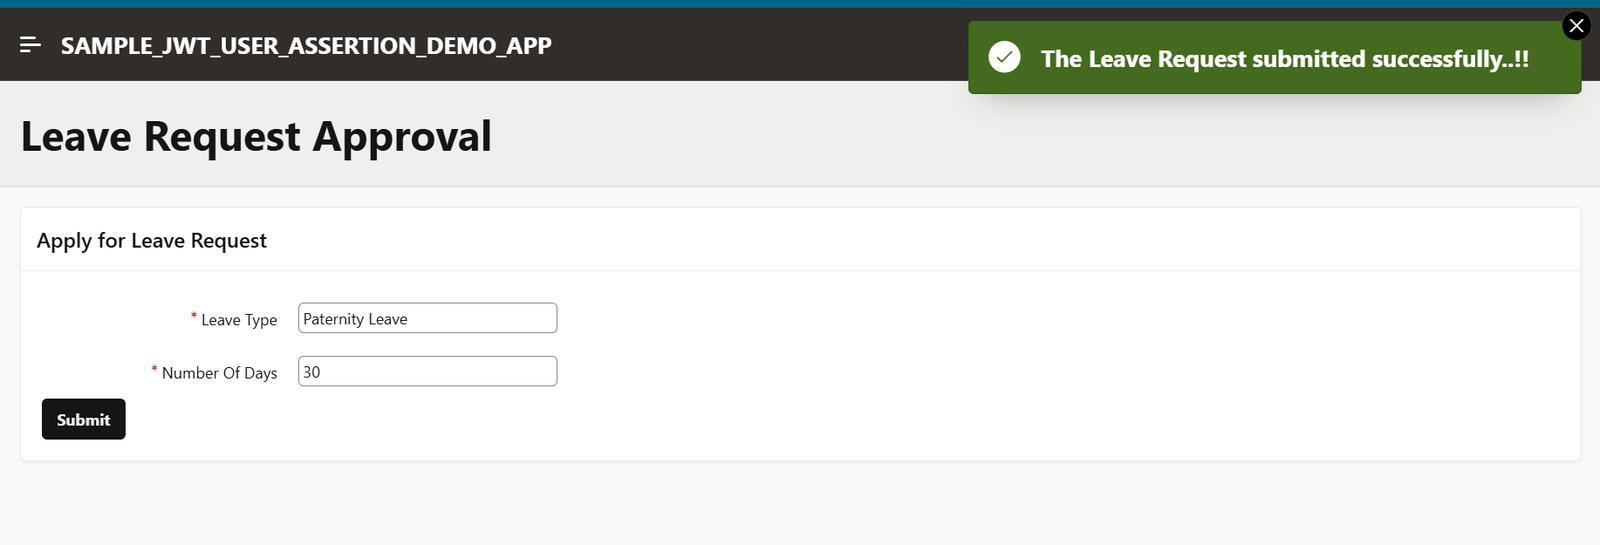
The request is submitted successfully in OPA.
Let us login to OPA with same OPA_1_INITIATOR@testmail.com user to check request initiated.


Here we can see request is created successfully from oracle APEX by OPA_1_INITIATOR@testmail.com user.
This request is assigned to APPROVAL_ROLE.
Let us login to OPA with OPA_2_APPROVER@testmail.com to check if request is in queue.
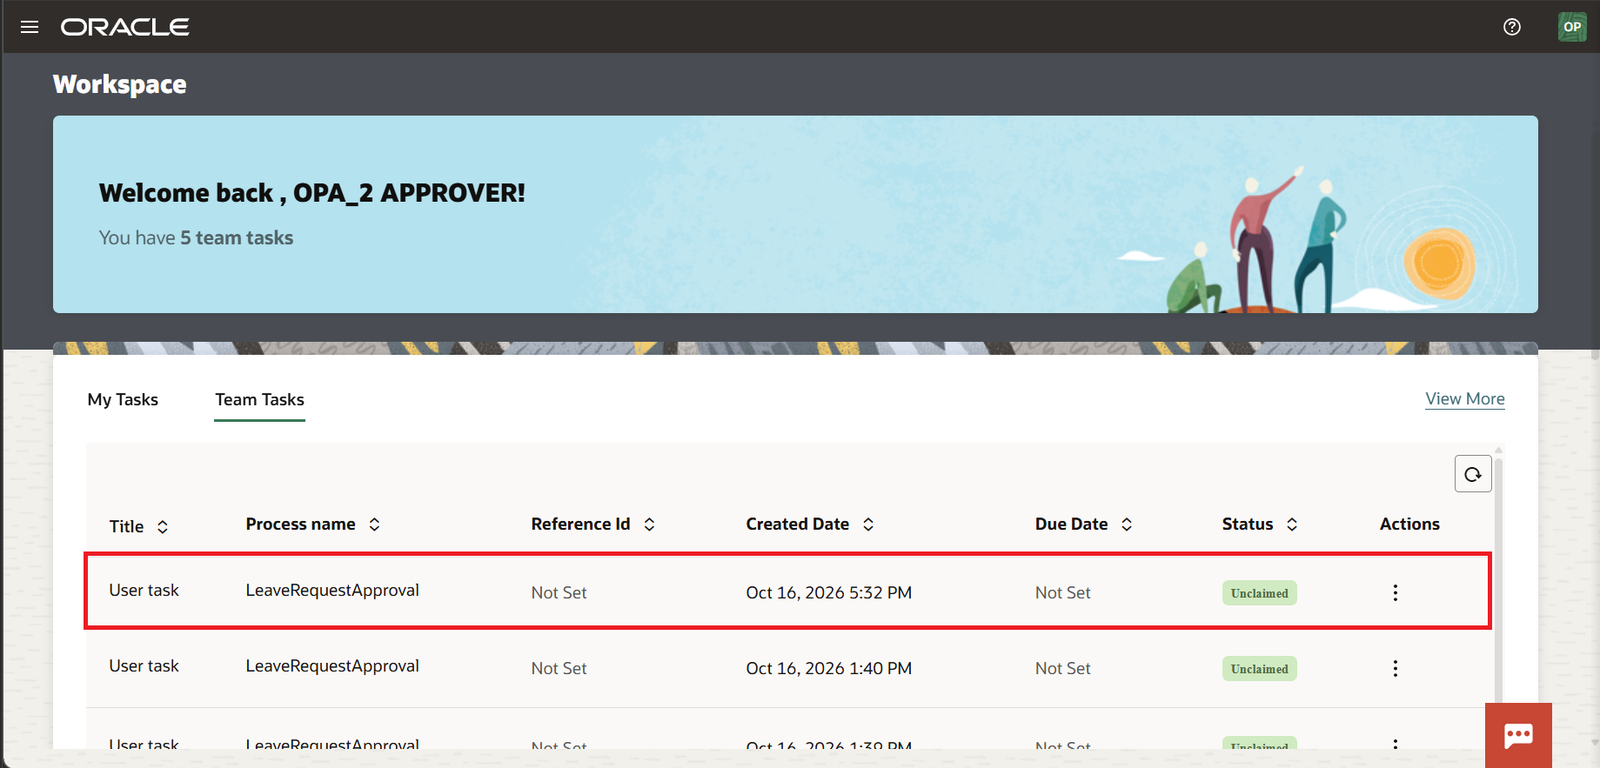

Copy this Task ID to approve it from Oracle APEX application.
Login to oracle APEX application using OPA_2_APPROVER@testmail.com user to approve the leave request.


Here provide TASK ID copied from OPA and click on Approve request.
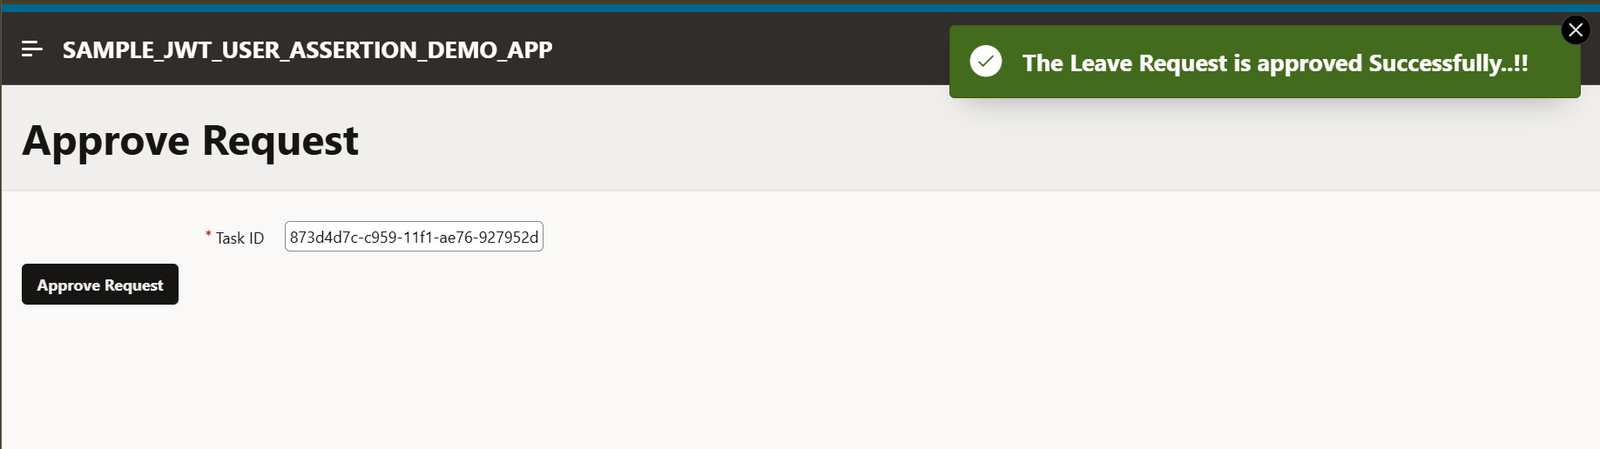
Now let us again check in OPA.
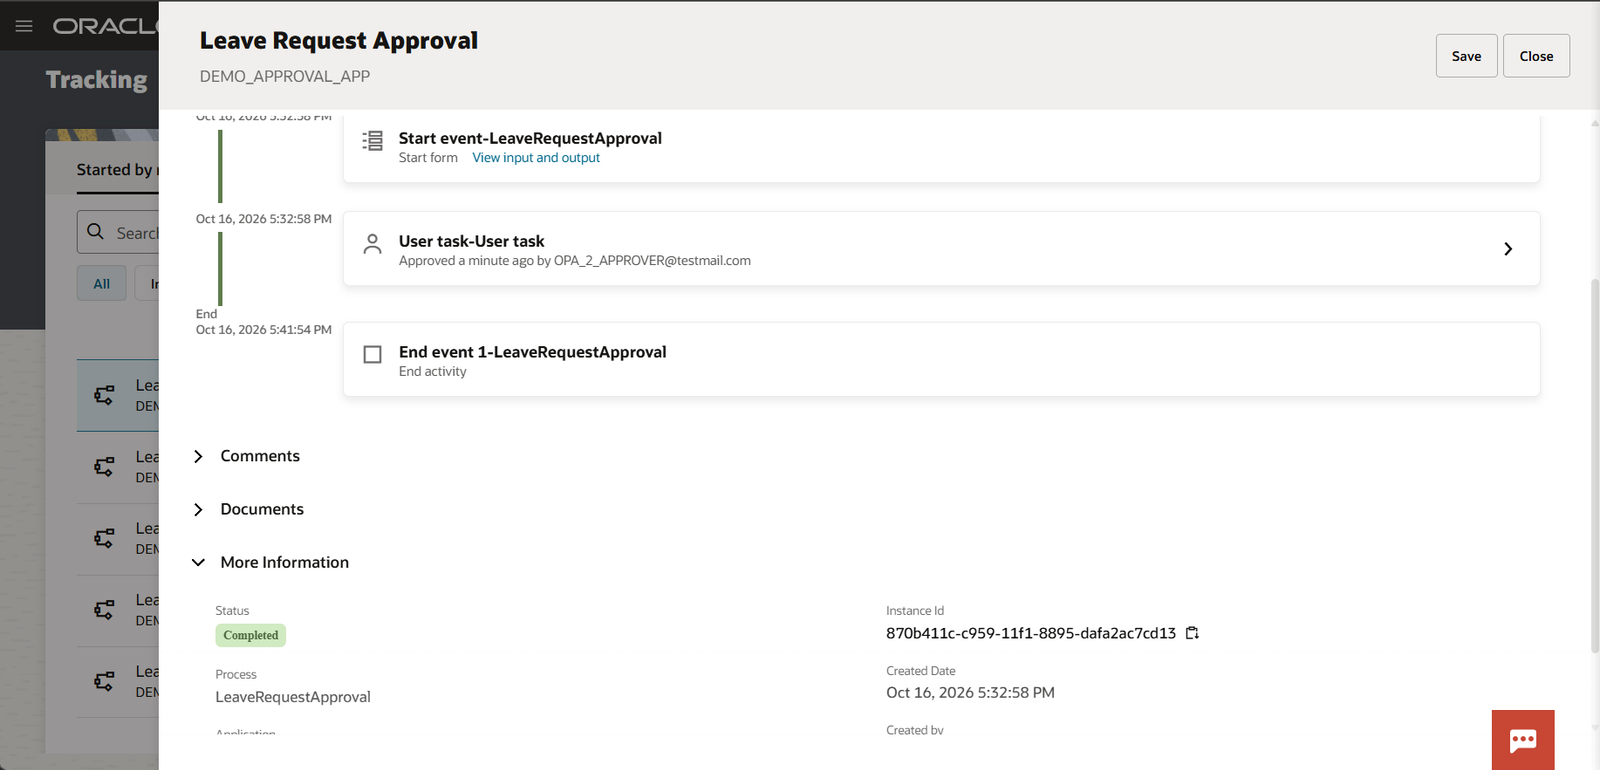
Process request in OPA is completed now.
